How to Check APK Certificate Fingerprint: A Complete Guide
Checking an APK certificate fingerprint is a useful step when you want to verify an Android app’s signing identity, compare different APK versions, or investigate whether a downloaded file comes from the expected developer. Although the process may sound technical, you can perform it with a few commands or a suitable APK analysis tool.
If you download APK files from sources outside Google Play, understanding certificate fingerprints can help you make more informed decisions before installing an application. However, a matching fingerprint alone does not guarantee that an app is safe or free from malware.
In this guide, you will learn how to check APK certificate fingerprint, which tools you can use, how to compare fingerprints, and what to do if two APK files show different certificate details.
What Is an APK Certificate Fingerprint?
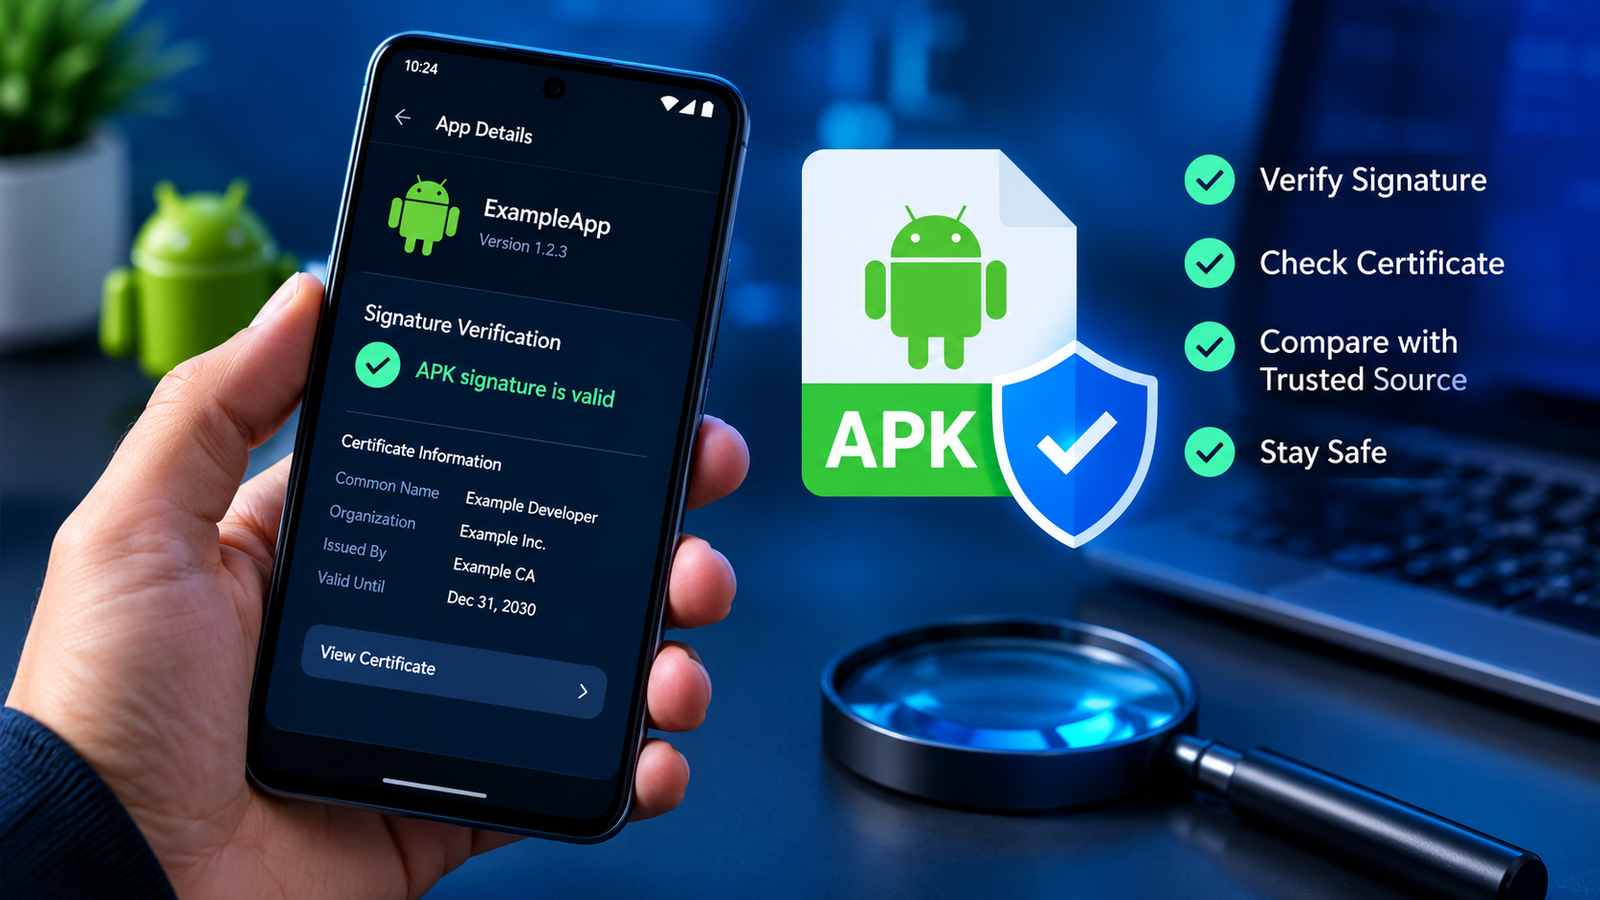
An APK certificate fingerprint is a value calculated from a digital certificate associated with an Android application’s signing identity. It is commonly displayed as a long hexadecimal string, often using the SHA-256 hashing algorithm.
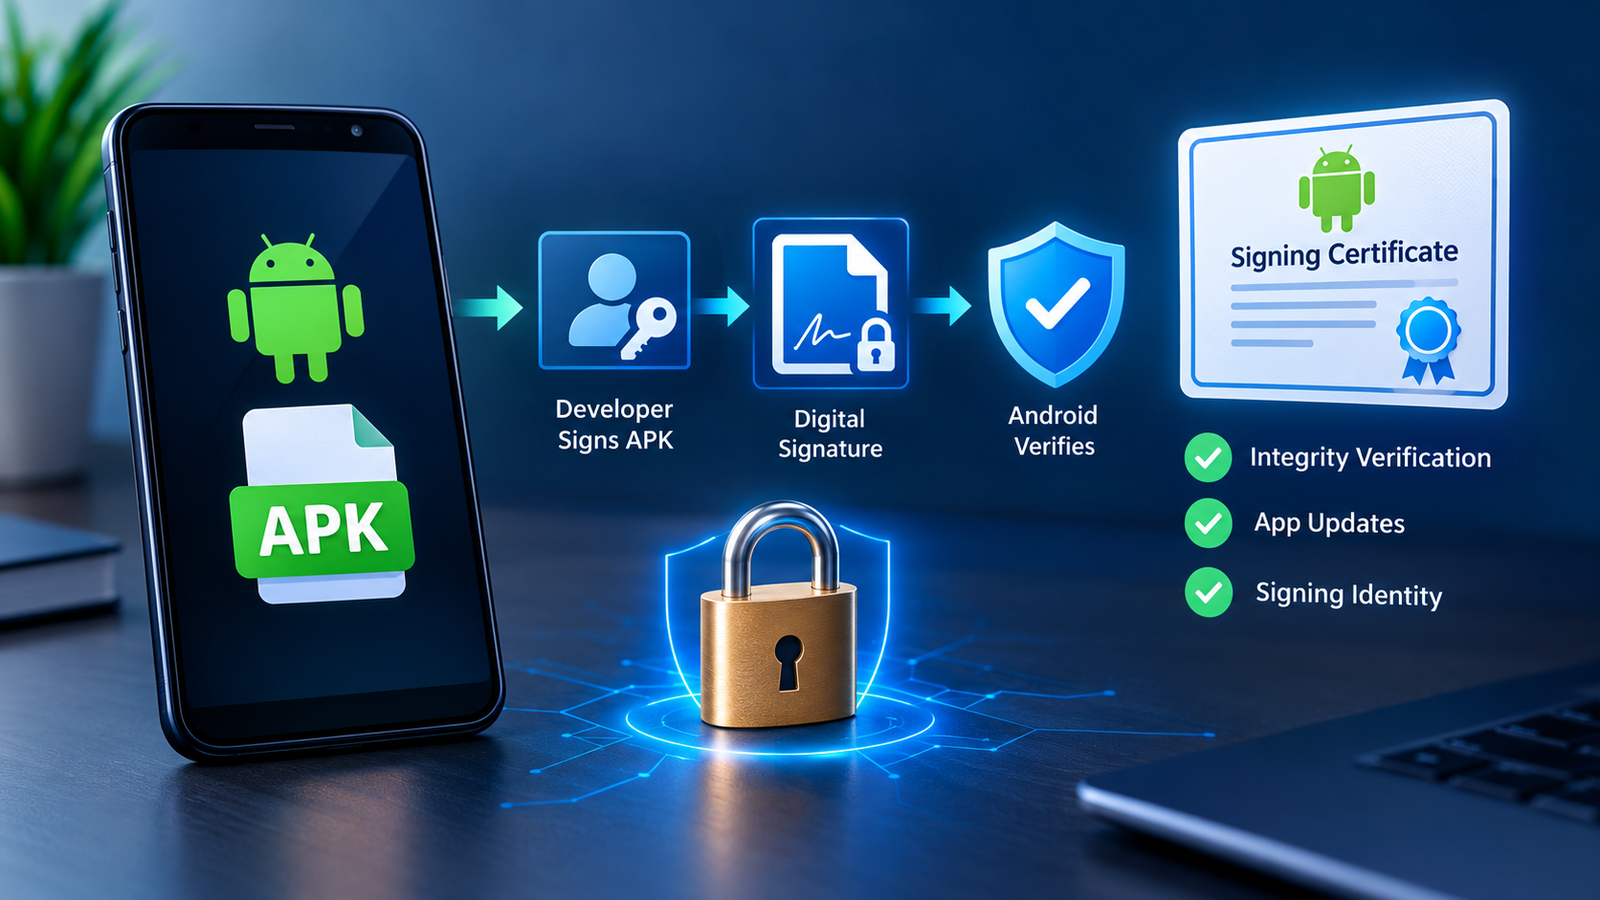
Android applications are signed with a digital signing key before distribution. The signature helps Android verify the integrity of the APK and determine whether an update has the expected signing identity.
A certificate fingerprint makes it easier to identify and compare that signing certificate.
For example, a SHA-256 fingerprint might look like this:
A1:B2:C3:D4:E5:F6:07:18:29:3A:4B:5C:6D:7E:8F:90:11:22:33:44:55:66:77:88:99:AA:BB:CC:DD:EE:FF
This is an illustrative example, not the fingerprint of a real application.
Why Does an APK Certificate Fingerprint Matter?
There are several reasons to check an APK’s certificate fingerprint:
- Verify signing identity: Compare the certificate with a trusted reference published by the developer.
- Compare app versions: Determine whether two APK files use the same signing certificate.
- Investigate modified APKs: Identify unexpected signing-certificate changes that may indicate repackaging.
- Troubleshoot installation problems: Understand why Android may reject an update signed with an incompatible key.
- Support app development: Check signing certificates when configuring app integrations that require a SHA-256 fingerprint.
Remember that a certificate identifies a signing identity, not necessarily the person or company behind it. A malicious developer can also sign an APK with a certificate.
How to Check APK Certificate Fingerprint Using apksigner
The Android SDK provides a tool called apksigner that can verify APK signatures and display information about the signing certificates. It is one of the most direct methods for checking an APK certificate fingerprint.
The tool is particularly useful for developers, security researchers, and users who are comfortable working with command-line utilities.
Step 1: Install or Locate Android SDK Build Tools
First, install Android Studio if you do not already have the Android development tools.
Open Android Studio and access the SDK Manager. Under the SDK Tools section, install Android SDK Build-Tools if necessary.
The apksigner executable is included in the Build-Tools directory.
On Windows, its location commonly resembles:
C:\Users\YourName\AppData\Local\Android\Sdk\build-tools\VERSION\
Replace YourName and VERSION with the appropriate values for your computer.
On macOS or Linux, the SDK is often located in an Android SDK directory under your home folder, although the exact path can vary.
Step 2: Locate Your APK File
Find the APK file whose certificate fingerprint you want to inspect.
For example, suppose the file is named:
sample-app.apk
Make sure you select the exact APK you intend to verify. If you have several versions of the same application, checking the wrong file can lead to an incorrect comparison.
It is also a good idea to keep the original download unchanged while examining it.
Step 3: Open a Terminal or Command Prompt
Open Command Prompt, PowerShell, or a terminal window.
Navigate to the directory containing the APK, or use the full path to the file in your command.
If the APK is stored in your Downloads folder, you can move to that directory before running the verification command.
Step 4: Run the Certificate Fingerprint Command
Use the following command:
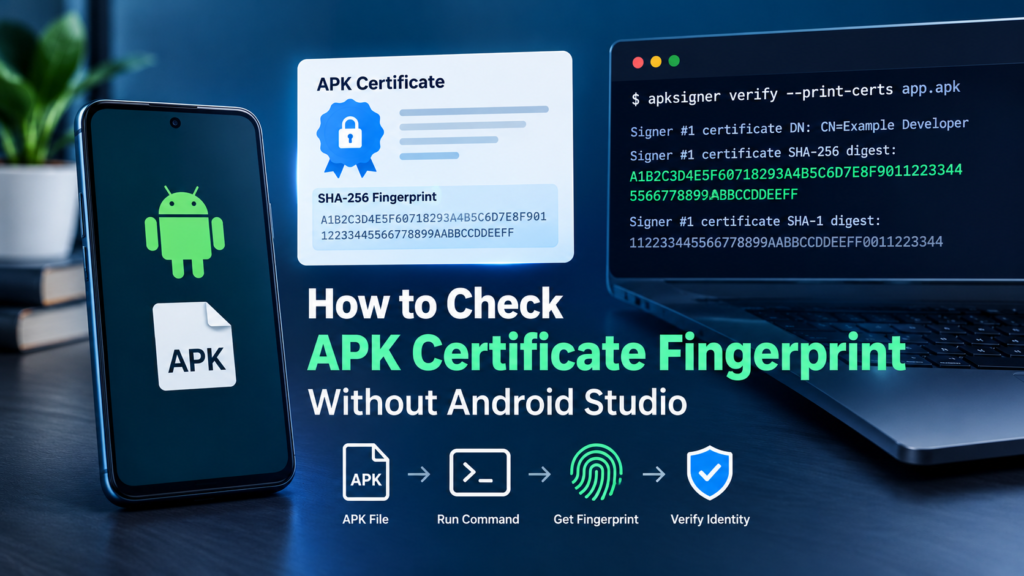
apksigner verify --print-certs sample-app.apkIf apksigner is not available in your system’s PATH, run it using its full executable path instead.
The command verifies the APK signature and displays information about its signing certificate. The output includes the certificate’s SHA-256 digest when available.
For additional diagnostic information, you can use:
apksigner verify --verbose --print-certs sample-app.apkThe verbose option provides more details about the verification process.
Android’s official documentation describes the --print-certs option as a way to display APK signing-certificate information. You can consult the official apksigner documentation for further details.
Step 5: Find the SHA-256 Certificate Digest
Look for output similar to the following:
Signer #1 certificate DN: CN=Example Developer
Signer #1 certificate SHA-256 digest: A1B2C3D4...
Signer #1 certificate SHA-1 digest: 11223344...
Signer #1 certificate MD5 digest: AABBCCDD...
The names and exact formatting can vary by tool version. The values shown here are illustrative.
Focus on the line labeled certificate SHA-256 digest if you need the SHA-256 fingerprint.
Copy the complete value and compare it with a trusted reference for the same application.
If the command reports a verification error, do not treat the displayed certificate information alone as proof that the APK is valid. Investigate the verification failure before trusting the file.
How to Check APK Certificate Fingerprint Without Android Studio
You do not necessarily need to open Android Studio every time you inspect an APK. Depending on your operating system and available tools, you can use other methods.
| Method | What you need | Best use |
|---|---|---|
apksigner | Android SDK Build-Tools | Checking APK certificates and signatures |
| Android Studio APK Analyzer | Android Studio | Inspecting APK contents and structure |
Java keytool | Java Development Kit | Inspecting a certificate file or keystore |
| Trusted APK analysis utility | A reputable analysis tool | A graphical alternative for certificate inspection |
Using Android Studio APK Analyzer
Android Studio includes APK Analyzer, which helps developers examine the structure and contents of an APK.
To use it:
- Open Android Studio.
- Find the option to analyze or profile an APK, depending on your version.
- Select the APK file you want to inspect.
- Examine the available APK information and signing-related details.
The exact interface can vary between Android Studio versions. For a definitive signature verification and certificate digest, apksigner verify --print-certs is generally the more direct choice.
Using Java Keytool
Java’s keytool utility can display certificate details, including SHA-256 fingerprints, when you have the relevant certificate or keystore.
For example, to inspect a certificate file:
keytool -printcert -file certificate.cerThis command examines the specified certificate file. It does not directly extract the signing certificate from an APK.
If your goal is to inspect an APK you downloaded, use apksigner or first extract the appropriate certificate with a suitable tool. Do not assume that inspecting an unrelated keystore or certificate gives you the fingerprint of the APK you are checking.
How to Compare Two APK Certificate Fingerprints
Comparing two fingerprints is useful when you want to check whether different APK versions use the same signing certificate.
For example, you might have one APK downloaded from a developer’s official website and another obtained from a third-party source.
Follow these steps:
- Run the certificate inspection command on the first APK.
- Copy its SHA-256 certificate digest.
- Run the same command on the second APK.
- Compare the complete SHA-256 values.
- Investigate any unexpected difference before installing or updating the application.
If both APKs report the same relevant signing certificate fingerprint, that is evidence that they share the same certificate identity.
If the fingerprints differ, the APKs may have been signed by different keys, may come from different distribution channels, or may reflect a legitimate signing-key change.
A difference does not automatically prove that an APK is malicious. Some developers change signing keys or use supported signing-key rotation arrangements.
What If the Fingerprints Do Not Match?
If the certificate fingerprints are different, consider the following possibilities:
- One APK has been repackaged and signed with another key.
- The files belong to different developers or application variants.
- The developer has changed signing keys.
- One file is an unofficial modification of the original app.
- You are comparing different certificates or signing identities.
Check whether the developer has published information about a signing-key change. If no reliable explanation exists, avoid installing the questionable file until you can establish its origin.
APK Certificate Fingerprint vs. APK File Hash
An APK certificate fingerprint and an APK file hash are different things. Confusing the two can lead to incorrect security conclusions.
A certificate fingerprint identifies a signing certificate through a cryptographic digest. An APK file hash, on the other hand, is calculated from the APK’s contents.
| Feature | Certificate fingerprint | APK file hash |
|---|---|---|
| What it identifies | A signing certificate | A specific APK file’s contents |
| Common algorithm | SHA-256 | SHA-256 |
| Same across app versions? | Often, if the signer remains the same | Usually not if the file changes |
| Useful for | Comparing signing identities | Checking file integrity against a trusted hash |
| Proves an APK is safe? | No | No |
For example, two APK files may contain different app versions but use the same signing certificate. Their certificate fingerprints may match even though their file hashes differ.
Conversely, two files containing the same application name may have different certificate fingerprints if they were signed using different keys.
For the most useful security check, examine both the signing certificate and the APK’s integrity where appropriate.
Common Mistakes When Checking APK Certificate Fingerprints
Even when you use the correct tool, a few mistakes can cause confusion.
Comparing SHA-1 With SHA-256
SHA-1 and SHA-256 fingerprints are different values. Make sure you compare the same algorithm on both sides.
If a developer publishes a SHA-256 fingerprint, do not compare it with the SHA-1 output from your APK inspection.
Trusting a Fingerprint From an Unknown Website
A website may display a fingerprint without explaining where it came from or how it was verified.
Whenever possible, obtain the reference fingerprint directly from the official developer’s documentation, a trusted developer-controlled channel, or another independently verified source.
A fingerprint is only useful for verification when the reference value itself is trustworthy.
Assuming a Matching Fingerprint Guarantees Safety
A matching certificate fingerprint does not prove that the APK contains no malware, has no security vulnerabilities, or behaves as expected.
It tells you that the signing certificate matches the reference you are comparing against. You should still consider the download source, requested permissions, file integrity, and the application’s reputation.
Modifying the APK Before Verification
Changes to a signed APK can invalidate its signature. Avoid editing or repackaging the file before checking its original signature.
If you need to investigate a modified APK, verify the exact file you received and interpret the result accordingly.
Best Practices for Verifying APK Certificates
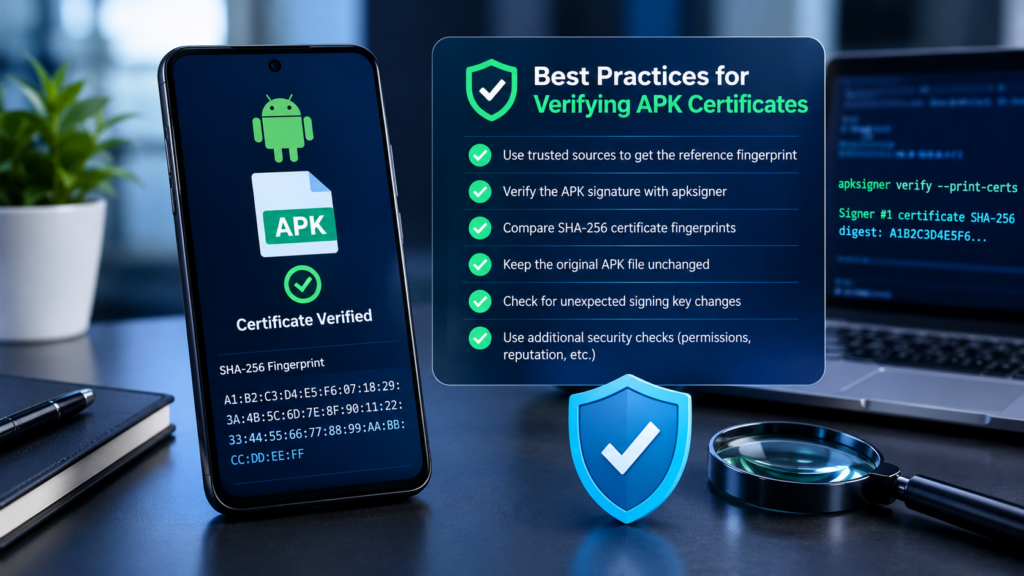
Use these practical guidelines when checking an APK certificate fingerprint:
- Download applications from official or otherwise reputable sources whenever possible.
- Use
apksignerto inspect the certificate and verify the APK signature. - Prefer SHA-256 when comparing certificate fingerprints, unless a particular integration explicitly requires another digest.
- Compare fingerprints against an independently trusted reference.
- Keep the original APK unchanged during verification.
- Investigate unexplained signing-certificate differences.
- Do not share private signing keys, keystore passwords, or other signing secrets.
- Remember that signature verification is only one part of assessing application security.
Following these steps can help you identify unexpected signing changes and avoid relying on an APK’s filename or icon as evidence of authenticity.
Frequently Asked Questions
1. How do I check an APK certificate fingerprint?
The simplest direct method is to use Android SDK Build-Tools. Run apksigner verify --print-certs your-app.apk and look for the certificate SHA-256 digest in the output. Compare it with a trusted reference for the same app.
2. What is the difference between SHA-1 and SHA-256 fingerprints?
Both are cryptographic digests calculated from a certificate, but they use different hashing algorithms and produce different values. SHA-256 is generally preferred for modern fingerprint comparisons unless a service specifically requires SHA-1.
3. Can I check an APK certificate fingerprint on Windows?
Yes. Install Android SDK Build-Tools, open Command Prompt or PowerShell, and run apksigner with the verify --print-certs options. You can use the full path to the executable if it is not available through your system’s PATH.
4. Does a matching APK certificate fingerprint mean the app is safe?
No. A matching fingerprint indicates that the certificate matches your trusted reference. It does not establish that the app is free from malware, vulnerabilities, or unwanted behavior. You should also check the source and other security indicators.
5. Why do two APK files have different certificate fingerprints?
The files may have been signed by different developers or keys, or one may have been modified and resigned. A legitimate signing-key change is also possible. Check the developer’s official information before concluding that a file is malicious.
6. Can I check an APK certificate fingerprint without Android Studio?
Yes. You can use apksigner from Android SDK Build-Tools without opening the Android Studio interface. Java keytool can inspect certificate files, but it does not directly extract an APK’s signing certificate from the APK itself.
Final Thoughts
Learning how to check APK certificate fingerprint gives you a practical way to examine the signing identity of Android applications. With apksigner, you can verify an APK signature, display its certificate information, and compare its SHA-256 fingerprint with a trusted reference.
The most important step is to compare the correct fingerprint against a reliable source. If the values differ, investigate the reason instead of immediately assuming that the APK is dangerous or legitimate.
Also Read: APKPure: A Complete Guide to Downloading Android Apps Safely

Post Comment